Find the gaps before attackers do.
Is your website, network or cloud infrastructure vulnerable to a cyber attack? Xanthus Security's certified testers think like adversaries so you can fix what matters first.
Two ways to see your organization through an attacker's eyes.
From a focused test of a single application to a full-scope adversary simulation, our engagements are scoped to your environment and delivered by people who do this every day.
Penetration testing
Web, network, cloud, Wi-Fi, ICS, IoT or any other kind of penetration test. Our team holds current certifications such as OSCP, GPEN, GWAPT, GMOB and CRTL, and has the depth to meet your requirements.
Every finding is confirmed by hand and exploited where it's safe to do so. You get a clear report that shows what an attacker could actually do, ranked so your team knows what to fix first. Available as a one-off test or as an ongoing service.
- Web apps
- Network
- Cloud
- Wireless
- ICS / IoT
- Social engineering
Red teaming
In-depth engagements that show the weaknesses in your enterprise from an outsider's perspective. Open-source intelligence, phishing, physical security and internet-facing attacks are just a few of the techniques we use.
Where a penetration test asks what's vulnerable, a red team asks whether a determined attacker could reach what matters most, and whether your team would notice. We measure your detection and response as much as your defences.
- OSINT
- Phishing
- Physical
- Detection & response
Trust us, and we deliver.
Your security is our top priority. We deliver a holistic, end-to-end service, from scoping through to a report your developers and executives can both act on.
- Manual, not just scanners. Every finding is confirmed by hand and exploited where it is safe to do so.
- Reports that drive fixes. Clear steps to reproduce, business impact and prioritized remediation.
- One-off or continuous. Point-in-time tests or penetration testing as a service on a schedule that suits you.
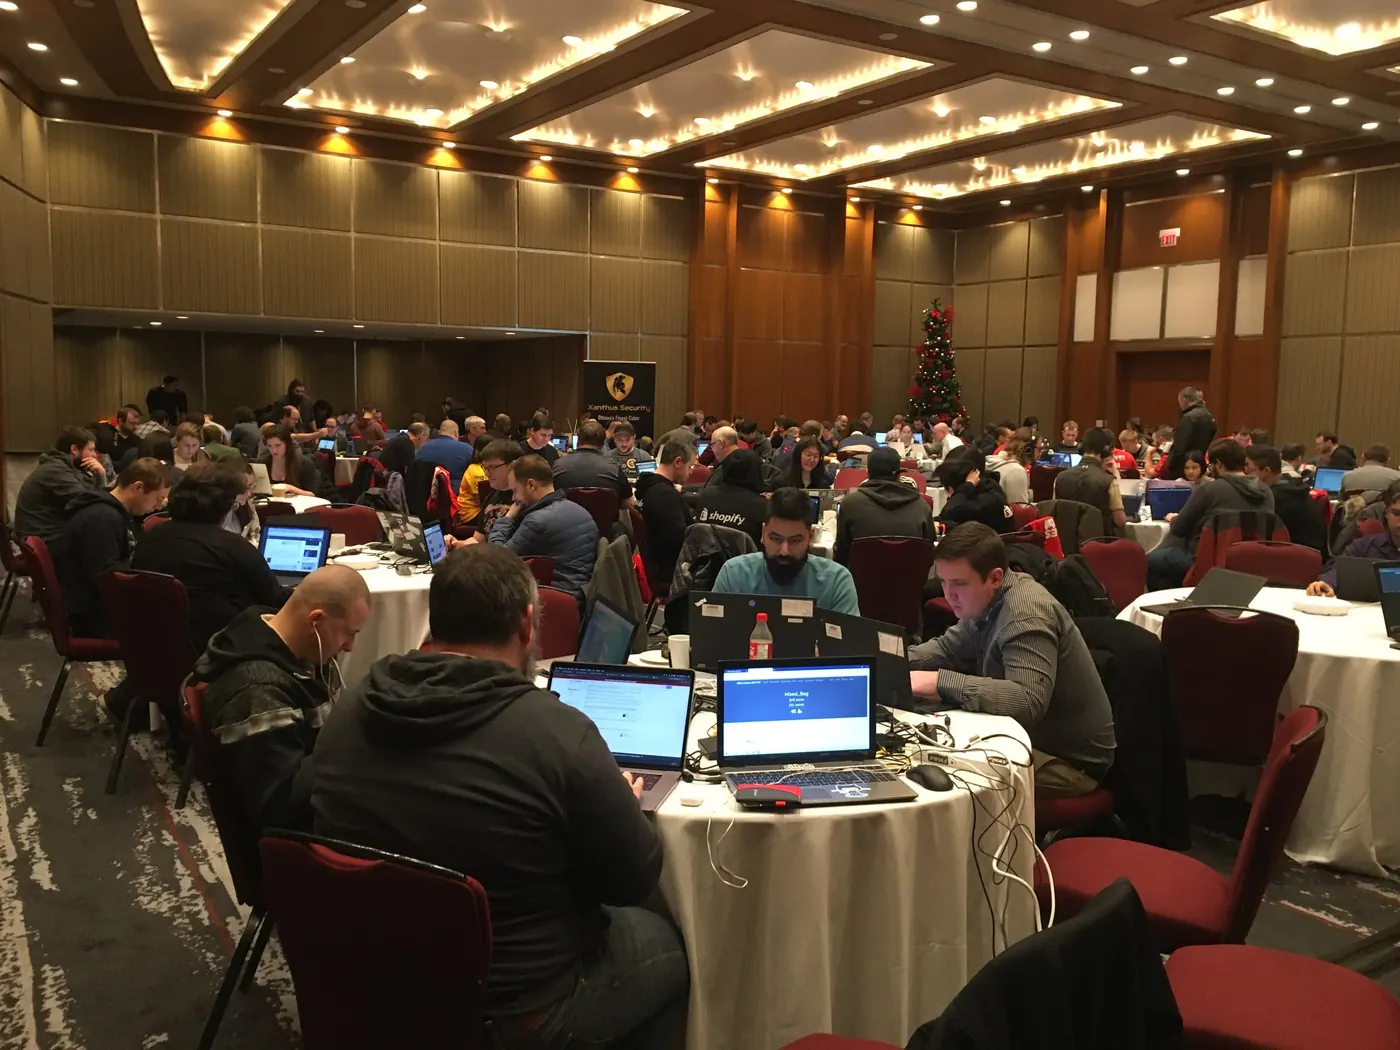
Growing the next generation of security talent.
Hands-on sessions built by practicing penetration testers, for teams levelling up and for students starting their careers.
Mentorship program
Four modules covering web, network, Active Directory and mobile testing, about 160 hours of guided, hands-on work, and an e-portfolio that shows employers what you can do.
Find out more
Training
Customized, hands-on training in vulnerability assessment and penetration testing for developers, IT and security teams, delivered online or at your workplace.
Find out moreResearch from our testers.
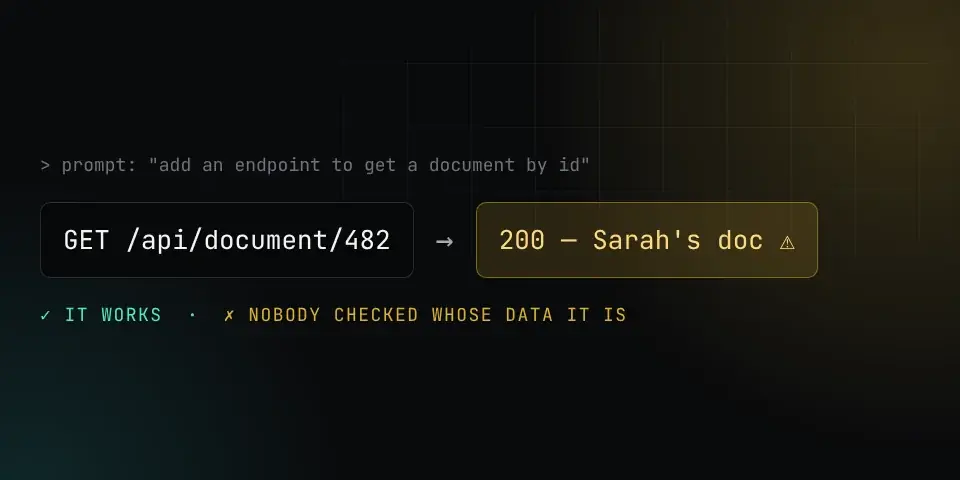
Vibe Coded, Not Vetted
AI assistants build features that work. In a recent assessment of a vibe-coded app, the same four security shortcuts kept showing up.
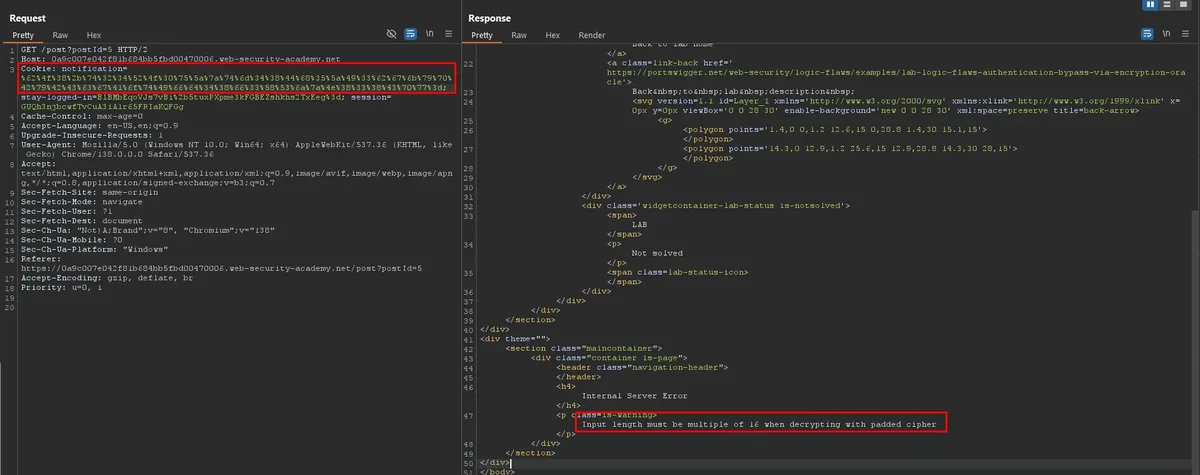
Cryptographic Failure Leading to Admin Account Takeover
From a real assessment: a flawed "stay logged in" cookie let a standard user forge a valid cookie for the administrator account.
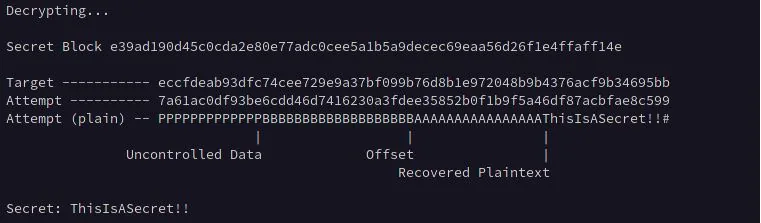
Attacking Electronic Codebooks
Why ECB mode should not be used to protect data, with a worked attack on AES in ECB mode you can adapt for your own proofs of concept.
Big enough to serve you, small enough to know you.
Tell us what you need tested. We'll come back with a clear scope and quote.